

A tailgating attack is a physical social engineering tactic in which an unauthorized person follows an employee through a secured door, gate, or turnstile without presenting their own credentials. It works because most people hold doors, avoid confrontation, and assume anyone who looks like they belong does belong.
Once inside, an intruder can steal devices, tamper with payment terminals, plug hardware into the network, or sit down at an unlocked workstation, which turns a simple courtesy into a data breach. The fix is a mix of entry controls that allow one verified person per credential, staff who feel comfortable challenging strangers, and device controls that limit what an intruder can reach after getting in.
What Is a Tailgating Attack?
Tailgating is the unauthorized entry of a person into a restricted area by following someone who has legitimate access. The intruder skips the badge reader, PIN pad, or guard check by slipping in before the door closes. Security teams classify it as physical social engineering because the attacker manipulates human behavior instead of defeating a lock.
So what is tailgating in cyber security, if the attack happens at a door? Physical access is often the shortest path to digital assets. An intruder inside an office can reach unlocked laptops, network ports, server closets, and printed customer records, which is why tailgating cyber security programs treat every entrance as part of the network perimeter.
The 2026 Verizon Data Breach Investigations Report found that 62% of breaches involved the human element, a category that covers errors, misuse, and social engineering. Tailgating belongs in that category because the attack only succeeds when a person lets it.
Tailgating vs. Piggybacking
The two terms are often used interchangeably, but security standards separate them based on consent. The comparison below shows how tailgating vs piggybacking scenarios differ in practice.
| Factor | Tailgating | Piggybacking |
|---|---|---|
| Does the authorized person know? | No. The intruder slips in unnoticed. | Yes. The employee knowingly lets the person in. |
| Typical tactic | Catching a closing door or following closely through a turnstile | Asking for the door to be held, usually with a cover story |
| Root cause | The access control system failed to detect a second entry | An employee made a judgment call under social pressure |
| Main defense | Turnstiles, vestibules, and anti-tailgating sensors | Training and a firm one-badge-one-person policy |
A piggybacking attack is harder to stop with hardware alone because the employee actively helps the intruder. Both scenarios end the same way, with an unverified person inside a space that was supposed to be controlled.
Why Tailgating Counts as Social Engineering
Tailgating social engineering relies on the same pressure points as phishing scams and voice phishing calls. Attackers count on courtesy, urgency, and the assumption that anyone who looks confident is authorized. That is why tailgating is classed as a social engineering attack even though no email or phone call is involved.
How a Tailgating Attack Works
Most tailgating attempts follow a short, predictable sequence. Knowing the stages helps staff spot an attempt before the door closes behind the intruder.
- Reconnaissance. The attacker watches the building to learn shift changes, busy entrances, smoking areas, and which doors employees prop open.
- Pretext. The attacker picks a role that explains their presence, such as a courier, contractor, new hire, or visitor running late.
- Entry. The attacker times the approach to follow a badge holder, often with full hands or a phone to the ear so a challenge feels rude.
- Objective. Once inside, the attacker steals devices or documents, installs hardware, photographs screens, or reaches a restricted room.
- Exit. The attacker leaves through a main exit, often before anyone realizes the visit was unauthorized.
The entry itself takes seconds, but every other stage gives staff a chance to notice something out of place. Training that covers the full sequence produces more useful reports than training focused only on the door.
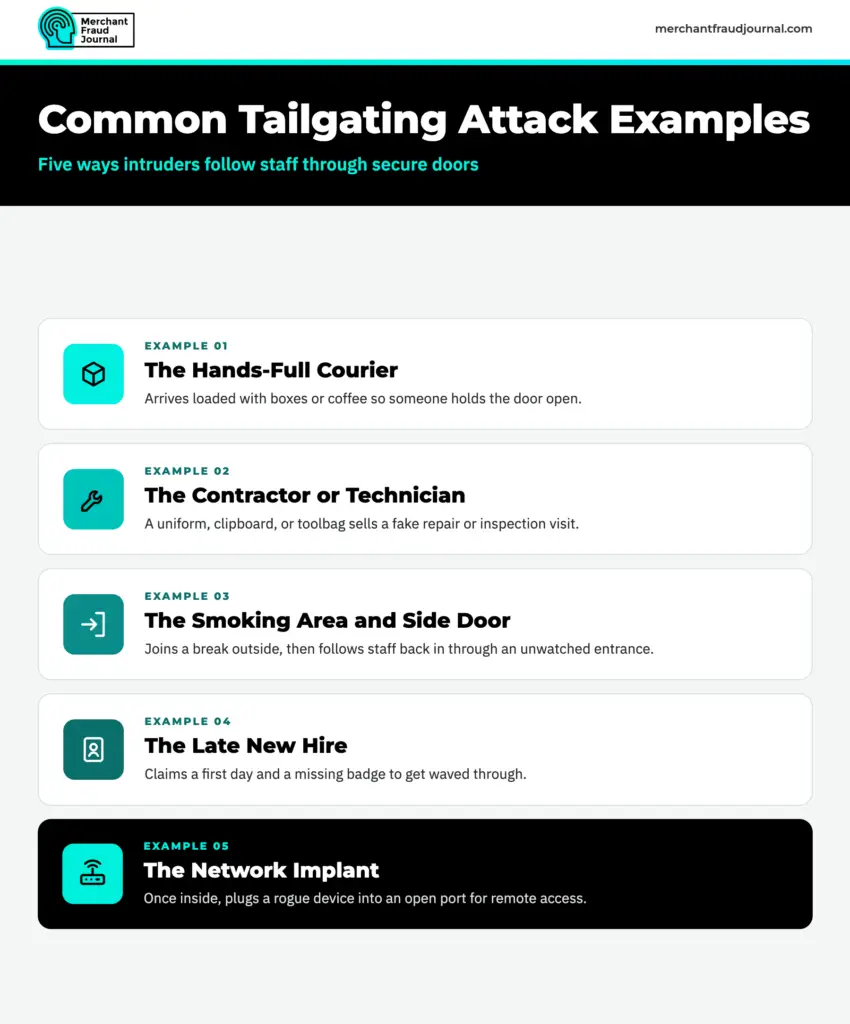
Common Tailgating Attack Examples
The scenarios below are the tailgating attack examples security teams run into most often. Each one relies on a normal workplace habit rather than a technical weakness.
1. The Hands-Full Courier
An attacker carrying boxes, coffee trays, or a large package waits near the entrance until an employee badges in. Holding the door for someone with full hands feels like basic courtesy, so few people ask for credentials.
2. The Contractor or Technician
Attackers dressed as HVAC technicians, IT support staff, or cleaning crews use a uniform and a clipboard as their pass. Employees rarely question a person who appears to be there to fix something, especially when the visit sounds routine.
3. The Smoking Area and Side Door
Side and back doors near smoking areas or loading docks are often propped open or lightly monitored. An attacker who joins a group on a break can walk back in with them.
4. The Late New Hire
An attacker claims to be a new employee who has not received a badge yet. The story is believable at companies with high turnover and frequent onboarding, and it invites coworkers to help.
5. The Network Implant
An attacker who tailgates into an office and plugs a small device into an open network port can give a remote team ongoing access to internal systems. This is a common example of tailgating in cyber security because the physical visit lasts minutes while the digital access can last for months.
A Real-World Case From 2026
In July 2026, a man followed an employee’s badge swipe into a restricted area at 30 Rockefeller Center in New York and confronted a television anchor before security detained him, according to an Alcatraz tailgating awareness survey release. The same release reported that 58% of Americans had never heard the term tailgating and 25% said they would likely let a stranger in if that person expected the door to be held.
These cases share one weakness. The door checks a credential, while the people around it are expected to check everything else.
Why Tailgating Matters for eCommerce and Retail Merchants
Merchants often treat fraud as an online problem, yet offices, stores, and warehouses hold the systems that run online sales. A successful tailgating attack can give an intruder direct access to several high-value targets.
- Admin sessions and dashboards. An unlocked laptop logged into a payment processor, storefront, or business email account can lead to account takeover attacks, refund abuse, or changed payout details.
- Payment terminals. An intruder with a few minutes in a back office or checkout area can tamper with or swap a point-of-sale device to capture card data, the in-store version of online web skimming attacks.
- Networks and devices. Hardware implants, keyloggers, and stolen laptops give attackers a foothold that skips perimeter defenses.
- Customer and cardholder data. Printed order records, dispute evidence files, and backup drives can expose personal data and trigger obligations under GDPR data breach rules.
- Inventory. Stockrooms and fulfillment centers are targets for direct theft, which later shows up as shrink or unexplained inventory gaps.
Card-handling merchants also have a compliance stake. PCI DSS physical security requirements (Requirement 9) direct merchants to restrict physical access to cardholder data, manage visitors, and protect point-of-interaction devices from tampering and substitution. An unchecked tailgating gap can therefore surface as an audit finding as well as a breach.
Who Is Most at Risk of a Tailgating Attack?
Any organization with controlled doors can be targeted, but risk rises wherever people expect to see unfamiliar faces.
- Large offices with high turnover, where employees cannot recognize every coworker
- Shared buildings and coworking spaces with several tenants and a single lobby
- Retail stores with back offices, cash rooms, or stockrooms near customer areas
- Warehouses and fulfillment centers with busy loading docks and seasonal staff
- Businesses with frequent contractor, courier, and vendor visits
- Hybrid workplaces with low daily attendance, where an empty floor gives an intruder time alone
The common factor is volume. The more unfamiliar people pass through an entrance each day, the easier it is for one more person to blend in.
How to Prevent Tailgating Attacks
Prevention works best in layers. Physical controls cut the number of attempts that succeed, while training and device controls limit the damage when one gets through. The steps below cover how to prevent tailgating at the building, team, and device level.
1. Add Friction at Entry Points
Anti-tailgating hardware makes it physically difficult for two people to pass on one credential. The right option depends on traffic volume and how sensitive the space is.
Turnstiles and access control vestibules
Optical turnstiles, speed gates, and security revolving doors let one person through per badge. For high-security rooms, NIST SP 800-53 security controls include PE-3(8), which describes access control vestibules where interlocking doors stop an unauthorized person from following an authorized one inside.
Sensors and video analytics
Overhead sensors and camera analytics can count people per badge swipe and alert security when the numbers do not match. Door-held-open and door-forced alarms add a second signal at side and back entrances.
2. Tie Every Entry to One Verified Person
Each entry should map to a single identity. Require visible photo badges, register and escort every visitor, and deactivate credentials the same day a worker or contractor leaves. For cash rooms, server closets, and secure stockrooms, add a second factor such as a PIN or biometric reader so a borrowed or cloned badge is insufficient.
3. Train Employees to Challenge Politely
Security awareness training should cover tailgating and piggybacking by name, with simple scripts staff can use without feeling rude. Offering to walk an unfamiliar visitor to reception keeps the exchange friendly while still stopping the entry.
Teach physical scenarios alongside lessons on how to spot a phishing scam so staff see tailgating as one more social engineering tactic. Make reporting quick and blame-free so employees flag attempts instead of ignoring them.
4. Limit What an Intruder Can Reach
Plan for the day someone gets through. Enforce automatic screen locks, a clean desk policy for printed customer data, and disabled or monitored network ports in public areas. Retailers should also inspect payment terminals on a set schedule for signs of tampering or substitution.
5. Test, Measure, and Fix
Physical penetration tests show how far an outsider can get without a badge. Track door-held alarms, visitor exceptions, and employee reports over time, then fix the entrances with the highest failure rates first.
Tailgating Prevention Controls at a Glance
The table below matches common controls to the problem each one solves and the sites where it fits best.
| Control | What it stops | Best fit |
|---|---|---|
| Turnstiles or security revolving doors | Tailgating at main entrances | Offices, data centers, and busy lobbies |
| Access control vestibules | Tailgating and piggybacking into high-security rooms | Server rooms, cash rooms, and secure stockrooms |
| Overhead sensors and video analytics | Undetected multi-person entries | Sites that cannot add physical barriers |
| Visitor management and escorts | Contractor and courier pretexts | Retail back offices, warehouses, and shared buildings |
| Security awareness training | Piggybacking driven by courtesy or pressure | Every organization |
| Screen locks and port controls | Data and network access after entry | Offices and checkout areas |
Most merchants will not need every control. Start with the entrances that lead to payment systems, customer data, and inventory, then extend coverage as budget allows.
Start Closing Tailgating Gaps This Quarter
A tailgating attack succeeds when a door relies on people to verify identity and people default to politeness. Map every entrance that leads to payment systems, customer data, or inventory, and decide which ones need a barrier, a sensor, or an escort policy. Train staff to badge in one at a time and to send strangers to reception, and lock down the devices an intruder could reach. Then test the setup with a physical assessment and fix the weakest door first.
Frequently Asked Questions
Tailgating is an example of what type of attack?
Tailgating is an example of a physical social engineering attack. It manipulates human behavior to gain entry, which places it in the same family as phishing, vishing, and pretexting.
What is an example of tailgating in cyber security?
A common example is an intruder who follows an employee into an office and plugs a small network device into an open port. The visit takes minutes, while the device can give attackers remote access to internal systems for months.
What is piggybacking in cybersecurity?
Piggybacking in cyber security usually means gaining physical access with an authorized person’s consent. The term also describes using someone else’s network connection or open session without permission, such as an unsecured Wi-Fi network or an unlocked computer.
Charity Amancio
Charity Amancio specializes in SaaS solutions for global eCommerce businesses, including payments and risk management applications. She bridges the gap between technology and merchant needs, offering practical perspectives on the tools shaping eCommerce. Her insights appear regularly in B2B publications covering the digital commerce space.
