

Summary
Account takeover fraud is when hackers illegally access another user's account, usually via stolen credentials. They then exploit that access for financial gain, such as making fraudulent purchases or stealing funds.
Account takeover fraud worries businesses more than ransomware now, with the majority of organizations reporting at least one incident. Fraudsters know how lucrative this type of attack can be. Hence, companies must ask themselves what account takeover is, how it impacts their business, and what they can do to protect themselves against it.
In this piece, you’ll learn how account takeover attacks happen, along with strategies that prevent them and detection methods that keep your accounts secure.
What Is Account Takeover Fraud?
Account takeover fraud occurs when criminals gain unauthorized access to your legitimate online accounts and use that control to commit financial or transactional abuse. Unlike simple credential theft where attackers merely obtain usernames and passwords, ATO represents the complete compromise and sustained control of your accounts. This allows attackers to operate undetected while appearing as trusted users.
When account takeover fraud happens, attackers exploit necessary credentials to drain funds, make unauthorized purchases, change your account details, or steal personal data. They can even sell your account information to other criminals. More than half of adults who’ve experienced identity fraud say it started with an account takeover.
Account takeover vs. account takeover fraud
Account takeover is the incident. Fraud is a potential risk. Not all account takeovers result in fraud events. If an attacker gains access to your company’s email account, there may be no intent to steal from you right away. The attacker might want to move laterally into other areas of your network, gather intelligence, or position themselves for a business email compromise attack.
Account takeover fraud takes ATO one step further and refers to attackers using that access to commit financial or transactional abuse. Financial abuse usually doesn’t stop after one transaction. Attackers steal loyalty points, modify stored payment information, or make purchases just below detection thresholds to keep their access open longer. These patterns can last for weeks before fraud teams notice them.
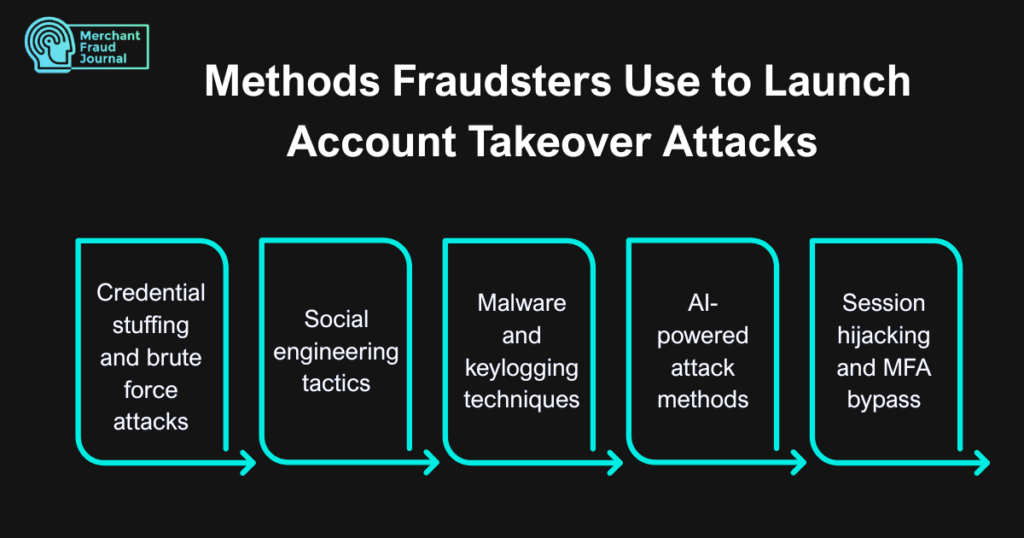
How Account Takeover Attacks Happen (Methods Fraudsters Use)
Attackers deploy multiple sophisticated methods to compromise your accounts. Each technique exploits different vulnerabilities in authentication systems and user behavior.
1. Credential stuffing and brute force attacks
Credential stuffing relies on automated injection of stolen username and password pairs into website login forms. Attackers acquire credentials from data breaches, password dump sites, or dark web marketplaces. They then use automated tools to test these stolen credentials on hundreds of websites.
The attack succeeds when you reuse passwords on multiple platforms. Success rates hover around 0.1%, meaning attackers compromise roughly one account per thousand attempts. Despite low individual success rates, massive credential collections containing millions or billions of login pairs make these attacks worthwhile.
Sample Case
The connected chain of breaches demonstrates this risk. Sony's database was compromised in 2011. Two-thirds of users whose data appeared in both the Sony breach and an earlier Gawker breach used the same passwords for both systems. Attackers then used these credentials against Yahoo in 2012 and Dropbox later. This created a cascading series of compromises.
Attackers test common password combinations and dictionary phrases until they find matches. Modern credential stuffing software uses bots to circumvent login protections. These bots attempt logins from IP addresses and device types of all kinds at the same time.
2. Social engineering tactics
Social engineering manipulates you into sharing credentials by impersonating trusted sources. The 2023 Verizon Data Breach Incident Report shows that 74% of all breaches include the human element. People are involved either via error, privilege misuse, use of stolen credentials, or social engineering.
Phishing occurs via email, smishing through SMS messages, and vishing through voice calls. CEO fraud involves impersonating executives to manipulate employees into fraudulent actions. Pretexting creates false urgency, such as claiming your account will be suspended unless you verify credentials right away. Baiting offers enticing rewards like free downloads or gift cards to extract your login information. Quid pro quo relies on bribery. SIM-swapping attackers are known to bribe mobile carrier employees.
3. Malware and keylogging techniques
Keyloggers record everything you type in secret. They capture passwords and personal data before encryption occurs. Snake Keylogger was first found in 2021 and remains one of the most prevalent threats. The malware performs keylogging, steals saved credentials, takes screenshots, and collects clipboard data. Attackers distribute keyloggers through phishing emails with malicious Office documents or PDFs that execute when you enable macros or use vulnerable software versions.
4. AI-powered attack methods
Artificial intelligence (AI) lets attackers create hyper-realistic phishing emails and scam messages. Fake login pages are now nearly indistinguishable from legitimate communications. Deepfake technology generates fake voices and video calls impersonating executives or customer service representatives. AI also helps attackers bypass CAPTCHA systems and evade fraud detection. Large-scale automated credential stuffing becomes easier.
5. Session hijacking and MFA bypass
Cookie theft allows attackers to hijack your active sessions by stealing session cookies valid for extended periods. Attackers bypass multi-factor authentication (MFA) checkpoints by importing harvested session cookies into their browsers. This lets them resume active sessions.
MFA fatigue involves bombarding you with repeated login verification requests. Frustration causes you to approve access eventually. Token theft exploits session cookies stored on your device and tricks browsers into authenticating attackers as trusted users.
How to Detect Account Takeover Fraud
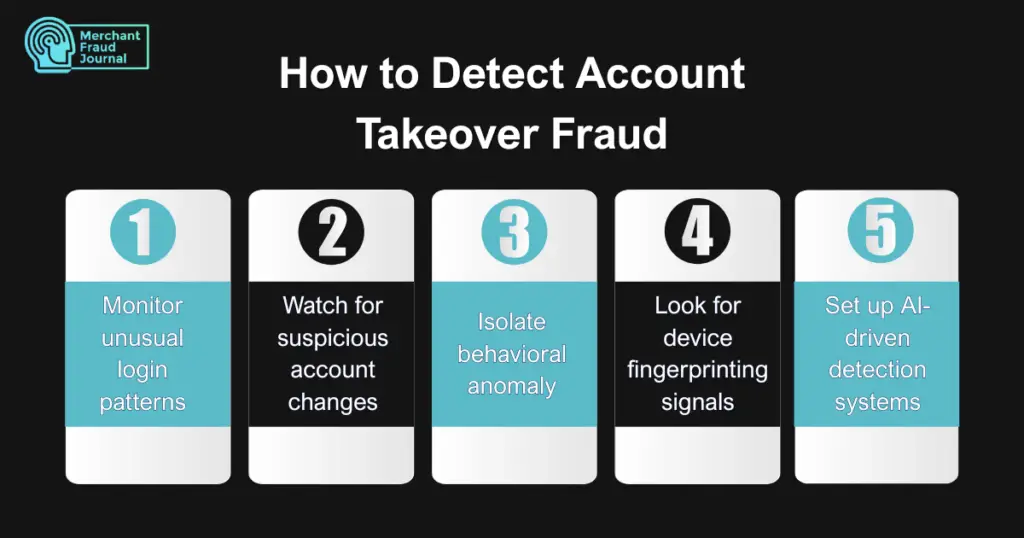
Early detection separates minor security incidents from catastrophic breaches. Spotting the warning signs of an ATO fraud requires monitoring multiple signals across different detection layers.
1. Monitor unusual login patterns
Failed login attempts from unfamiliar locations signal potential compromise. A series of blocked logins indicates attackers testing credentials, especially during unusual hours or from unexpected geographic locations. Impossible travel scenarios provide clear evidence, as when the same account logs in from New York and then Warsaw two hours later. Login speeds that appear too fast or device fingerprints that don’t match previous sessions reveal automated attack tools at work.
2. Watch for suspicious account changes
Password reset emails you didn’t request often mean someone is attempting access. Check for updates to recovery options like added phone numbers or alternate email addresses, which attackers use to secure their own access.
Email forwarding rules that weren’t created by you allow attackers to monitor incoming messages without alerting you. Missing emails and unexpected MFA requests can indicate tampering, along with changes to notification preferences.
3. Isolate behavioral anomaly
User and entity behavior analytics establish baselines for normal activity and then flag deviations. Peer group behavior comparison measures individual actions against similar users and identifies anomalies like accessing IP addresses on other group member visits.
Rare behavior detection spots most important changes in data download volumes or access patterns. To cite an instance, baseline analysis showing an average of five failed logins daily but suddenly recording 135 attempts clearly indicates deviation from standard behavior.
4. Look for device fingerprinting signals
Device fingerprinting examines hundreds of data points including browser plugins, OS settings, and screen resolution to identify returning users with 99.5% accuracy. This technology detects fraudsters attempting to go undetected by clearing cache, switching browsers, using incognito mode, or employing spoofing tools.
5. Set up AI-driven detection systems
Machine learning analyzes massive data volumes with up-to-the-minute analysis and detects suspicious behavior patterns that humans might miss. AI-driven systems identify combinations of anomalies that signal compromise when linked together, such as a suspicious login paired with new OAuth (open authorization) and external email forwarding.
What Industries Are the Most Vulnerable to ATO Attacks?
ATO attacks impact nearly every industry, though some face significantly higher exposure due to the nature of the data and assets they hold. The financial gain, sensitive data, and operational dependencies attackers can exploit vary widely from sector to sector.
- Financial services: This sector represents 32% of breaches, as attackers drain balances, set up unauthorized instant payment beneficiaries, or use accounts as mules for layered crypto-laundering. Unauthorized wire transfers and payment manipulation make it a prime target for direct monetary gain.
- eCommerce and retail: Fraudsters capitalize on stored payment methods, abuse gift cards, and execute eCommerce fraud. Social media and retail combined account for 51% of breaches, with attackers using compromised social accounts for long-term pig butchering crypto scams or draining stored credit cards on ecommerce platforms.
- Healthcare: Organizations must balance patient care access with security requirements, leaving them exposed to medical identity theft, fraudulent insurance claims, and benefits exploitation.
- SaaS and cloud services: Attackers target stored data, administrative control, and API credentials in software-as-a-service (SaaS) platforms to launch further attacks. This susceptibility is driven by diverse user populations, limited security budgets, and collaboration requirements.
These figures show that vulnerability isn’t confined to one type of organization. Whether the motive is direct financial theft, data exploitation, or a foothold for larger attacks, every industry has a stake in strengthening its account security.
Empowering Your Shield Against Account Takeover
Your best defense against account takeover fraud combines strong authentication, continuous monitoring and user awareness training. Start by implementing multi-factor authentication in accounts of all types and educate your team about phishing tactics. Deploy behavioral detection systems and other layers of fraud protection. Organizations that take proactive steps now will be better positioned to prevent losses. Prevention costs less than recovery after a successful attack.
Frequently Asked Questions
What's the difference between account takeover fraud and identity theft?
Account takeover fraud involves hijacking an existing account using stolen login credentials, while identity theft involves using someone's personal information to create new accounts or lines of credit. ATO is often a precursor to broader identity theft once the attacker has access to additional personal data.
How do businesses recover from a wave of account takeover attacks?
Recovery typically involves resetting affected credentials, strengthening authentication requirements, and reviewing security infrastructure for gaps. Many businesses also invest in fraud detection tools to prevent repeat incidents.
How does account takeover fraud affect customer trust?
Customers who experience an account takeover often lose confidence in a company's ability to protect their data. This can lead to customer churn, negative reviews, and long-term reputational harm for the business.
Charity Amancio
Charity Amancio specializes in SaaS solutions for global eCommerce businesses, including payments and risk management applications. She bridges the gap between technology and merchant needs, offering practical perspectives on the tools shaping eCommerce. Her insights appear regularly in B2B publications covering the digital commerce space.